Audit Proof Open Banking Consent Management for Engineers
Audit Proof Open Banking Consent Management for Engineers
Open banking consent management is the system that requests, records, enforces, refreshes, and revokes a customer’s permission to share financial data with third parties. The design imperative that matters most: build it as a continuous lifecycle, not a one-time checkbox, controlled through a transparent dashboard and backed by auditable consent objects. Everything in PSD2, GDPR, and CFPB guidance flows from that single idea, and so does every SCA flow and Data Cluster you’ll build around it.
TL;DR:
- Ensuring continuous lifecycle management, including refresh and revoke features, is crucial for compliance and preventing audit failures, beyond initial consent creation.
- Transparency at capture requires showing the TPP’s registered name, explicit purpose, specific data scope, and consent duration, with documented audit trails for every event.
- Building a user-friendly consent dashboard that displays active consents and allows instant revocation improves customer trust and reduces accidental consent lapses.
- Implementing strict API controls with consent ID, scope, recurrence, and expiry fields, along with webhook-based status sync, enforces consent rules reliably in production.
- Automated oversight, including logs, monitoring revoke patterns, and handling credential breaches, ensures ongoing operational compliance and mitigates risks.
Table of Contents
- How does the open banking consent lifecycle actually work?
- What does regulatory transparency actually require at consent capture?
- How should the consent dashboard and revocation flow work?
- Which API fields and flows do engineers need to build?
- What operational controls keep consent management compliant over time?
- How does an AI-native API platform support these controls?
- What should you prioritize first when building this?
- How Jundago fits into your consent management build
- Sources
How does the open banking consent lifecycle actually work?
A consent record isn’t a permission you set once. It’s a living object that moves through distinct states, and each state has its own API calls and UX moment. Miss one, and you either fail an audit or lock a customer out of a service they thought they’d already approved.
Here’s the sequence engineers and product teams need to implement:
- Create the consent object. Define the explicit purpose, the access scope, and a
validUntiltimestamp before anything reaches the customer. - Present the capture screen. Show the trading name of the third-party provider (TPP), the purpose, the exact data scope, and the consent duration, in that order, before redirecting to authorization.
- Run Strong Customer Authentication (SCA). Redirect the customer to their bank’s authorization flow, then persist the returned
consentIdandscaStatus. - Enforce at access time. Every data pull checks the stored consent against its scope and expiry before returning anything.
- Support refresh cycles. Recurring consents need a
recurringIndicator, afrequencyPerDaycap, and a reconfirmation prompt, commonly every 90 days. - Build revoke and status endpoints. A Get Consent Status call and webhook notifications keep both the bank and the TPP synchronized when a customer pulls the plug.
Treat this as a product, not a feature. The lifecycle only holds together if refresh and revoke are as well built as creation. Most implementations get step one right and then bolt the rest on later, which is exactly where audits find gaps.
What does regulatory transparency actually require at consent capture?
Regulators don’t just want consent, they want proof the customer understood what they agreed to. That distinction shows up in Open Banking Standards’ data management guidance, which flags missing transparency details as one of the most common compliance failures.
Build your checklist around these non-negotiables:
- Display the TPP’s registered trading name, not a legal entity name buried in fine print.
- State the specific purpose of the data request in plain language.
- List the exact data scope requested, not a vague category.
- Show the consent duration and what happens when it lapses.
- Log and retain audit evidence of every consent capture and revocation event.
- Handle periodic reconfirmation windows and document why the interval was chosen.
Incomplete disclosure at the point of capture is a frequent cause of open banking compliance issues, according to the transparency requirements outlined by Open Banking Standards. That’s not a UX nitpick. It’s the single most preventable audit finding in this space.
Jurisdiction matters here too. PSD2 and the UK’s Open Banking regime set the 90 day reconfirmation norm, GDPR governs the broader data-processing lawful basis, and the CFPB’s personal financial data rights framework approaches consumer data access from a different regulatory angle entirely. Never assume one region’s checklist transfers cleanly to another. When you hit an edge case, an implementation is genuinely international, or you’re not confident which regime governs a specific data flow, go to the primary standard or a qualified compliance counsel before shipping.
How should the consent dashboard and revocation flow work?
Customer research consistently points to one conclusion: the dashboard is the control plane. Open Banking Standards’ customer experience guidelines describe it as a remote control, and that’s the right mental model. If a customer can’t find it, understand it, or act on it in under thirty seconds, the dashboard has failed regardless of how compliant the backend is.
A working dashboard needs to:
- List every active consent with the TPP’s brand name, purpose, and expiry date visible at a glance.
- Group technical permissions into human readable Data Clusters, since OBIE research shows raw permission strings confuse most users while grouped categories don’t.
- Allow drill-down from a cluster to the specific permission underneath, for the minority who want the detail.
- Support one-tap revocation with immediate effect, not a support ticket.
- Send a confirmation receipt and explain exactly what stops working once access ends.
Pro Tip: Send a reconfirmation reminder five to seven days before a 90 day window closes, not on the expiry date itself. A same-day notice reads as an outage to most customers, not a routine renewal.
Dashboards with clear revocation paths measurably increase customer trust, and that trust is what keeps customers opting into open banking products instead of abandoning them after one confusing renewal notice.
Which API fields and flows do engineers need to build?
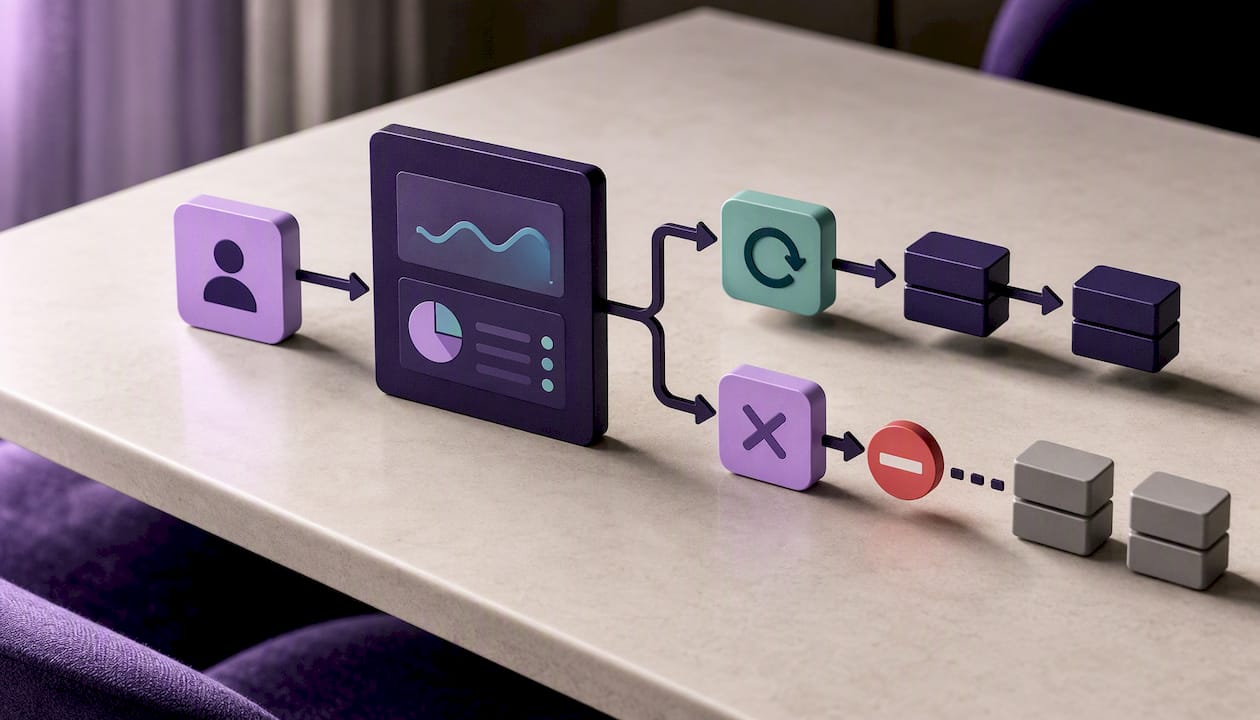
The dashboard is the surface. Underneath it sits a set of API primitives that either enforce the promise made on screen or quietly fail to. Open Payments’ consent creation documentation lays out the core object structure most open banking APIs converge on:
| Field | Purpose |
|---|---|
consentId |
Unique identifier persisted after SCA completes |
PSU-ID |
Correlates the consent to the specific customer |
access |
IBAN list or permission cluster the consent covers |
recurringIndicator |
Marks whether the consent supports repeat access |
frequencyPerDay |
Caps how many times data can be pulled daily |
validUntil |
Hard expiry timestamp enforced server side |
Three implementation patterns determine whether this holds up in production:
- SCA flow selection. Redirect flows send the customer to the bank’s own authentication page; decoupled flows push approval to a separate device or app. Either way, capture and store the resulting
scaStatusimmediately, since a partial SCA state left unhandled is a common source of stuck consents. - Least-privilege token design. Scope tokens tightly to the approved
accessobject, enforcefrequencyPerDayserver side rather than trusting the client, and set refresh windows that matchvalidUntilrather than a generic default. - Status synchronization. Prefer webhooks over polling for consent status changes, use idempotent create-consent calls so retries don’t spawn duplicate records, and attach an
X-Request-IDheader to every call for correlation during incident review.
Some teams explore blockchain based ledgers for immutable consent audit trails. The trade-offs are real: added latency, unresolved privacy questions, and uncertain legal admissibility in most jurisdictions make it a research direction more than a production pattern today.
What operational controls keep consent management compliant over time?
Building the lifecycle correctly on day one buys you nothing if nobody watches it on day two hundred. Every consent event needs a log entry capturing the exact page version the customer saw, the timestamp, the PSU-ID, the consentId, and the resulting scaStatus. That log is your evidence when a regulator or a customer disputes what was disclosed.
Retention policy needs a clear split: delete personal data tied to lapsed consents on schedule, but retain the audit trail proving what was captured and when, since the evidence often needs to outlive the consent itself.
- Monitor for stale consents approaching their reconfirmation window.
- Track revoke rates by TPP to spot patterns worth investigating.
- Flag failed authorization attempts and access patterns that don’t match historical usage.
- Have a coordinated disclosure path ready with ASPSPs and TPPs if a credential or token is compromised.
Pro Tip: A sudden spike in revocations tied to one TPP is almost always a UX problem on their end, not a customer sentiment shift. Investigate the integration before assuming churn.
How does an AI-native API platform support these controls?
Building every one of these lifecycle stages by hand, across REST and GraphQL endpoints, is where most compliance timelines slip. Jundago generates consent-aware APIs directly from intent, then attaches policy-as-code rules and RBAC/ABAC enforcement at the gateway layer so scope checks happen automatically rather than getting re-implemented per endpoint.
That structure supports:
- Audit trails and governance streamed to a compliance store without custom logging code per service.
- Multi-cloud deployment across AWS, Azure, GCP, and Oracle Cloud with the same policy set enforced everywhere.
- Automated testing of consent enforcement paths before anything reaches production.
What should you prioritize first when building this?
Ease of revocation beats almost every other design decision here. Get that wrong and no amount of clever data clustering saves the experience. Favor Data Clusters for what customers see and raw API permissions for what your systems enforce. Automate refresh reminders and monitoring early. Manual compliance tracking doesn’t scale past your first few dozen integrations.
— vivek
How Jundago fits into your consent management build
If you’ve read this far, you already know the hard part isn’t deciding what a compliant consent flow looks like. It’s building the enforcement layer fast enough that engineering doesn’t become the bottleneck on your compliance timeline. Jundago maps directly onto the controls covered above: policy-as-code for consent rules, RBAC and ABAC for scope enforcement, built-in audit trails, and API generation that produces consent-aware endpoints instead of retrofitting checks after the fact.
A practical starting point looks like this: run an architecture review against your current consent flow, pilot one consent-aware endpoint through Jundago’s generation pipeline, and check the result against the transparency checklist covered above. For teams juggling account aggregation use cases, a family office platform’s approach to bank account aggregation shows how consent scope decisions play out in a real multi-account context. If your consent architecture spans regions, the data residency trade-offs in SaaS compliance are worth reviewing alongside your retention policy. When you’re ready to see how policy-as-code enforcement works against your own consent objects, request a demo of Jundago and bring your current API schema.